Friday, November 24, 2006

A Zune tip and some minor disadvantages.

This very useful information was spotted at the techmeme site today and I thought about sharing it with you guys incase you happened to miss it. A feature that is missing in Zune and that is available with almost every other MP3 players is the option to use it as an external hard drive. Now thankfully this can be taken care
of. Read on.

How to copy data off your Zune (How to use it as an external hard drive) .

This was posted orginally by Dan in his phaleux.com blog.

Dan highly recommends backing up the registry values mentioned below in the steps before modifying anything. If you don’t know how to do that, he does not recommend that you even attempt this right now.

1. Make sure your Zune is not plugged in and your Zune software isn’t running
2. open up regedit by going to the start menu and selecting “run”. Type regedt32 and hit “OK”
3. Browse to HKEY_LOCAL_MACHINE\System\ControlSet001\Enum\USB\
4. Search for “PortableDeviceNameSpace”. This should be contained in the
Vid_####&Pid_####\########_-_########_-_########_-_########\ Device Parameters within the above …\USB\ The ##’s listed here will be numbers and letters specific to your Zune
5. Change the following values:

  • EnableLegacySupport to 1
  • PortableDeviceNameSpaceExcludeFromShell to 0
  • ShowInShell to 1

6.
Plug in your Zune, and make sure the Zune Software starts up.
7. Hopefully at this point you can open up “My Computer” and browse your device, though it does NOT show up as a drive letter.


Okay, to add on to this above mentioned disadvantage (which can now be taken care of by using the above mentioned steps let me share with you some other minor disadvantages that was spotted with Zune by one of the Cnet editors.

  • When music is transferred from one Zune to another the song that is being played on the recipient Zune is interrupted and it asks whether to accept the transfer or not. If it is accepted the transfer starts and the song was being played stops and this can be irritating.
  • It is not possible to send more than one song for a while.
  • There is no custom equalizer. Also if you have to change the pre-set set of equalizers one has to go all the way back to preferences and change it and that means if you are listening to a song and want to change the settings for example from Rock to Pop while listening to the song it is not possible.
  • The wireless mode takes up a lot of battery power. So if you want to play a game or something then you have to turn off the wireless mode to preserve the life of the battery. So if you want to be always available but at the same time do some stuffs on your Zune you would be burning up the battery power. So it is advised to turn on the wireless mode only if you need the wireless and otherwise while you are doing stuffs on your Zune like playing games you have to turn it off to conserve battery power. This is the Zune paradox.
Overall this is a great device except for these minor flaws.

Related Reading:-
Useful links with tips for Zune users.

Everthing about Trojans and Anti Trojans.


Well, everyone has heard of Trojan horses, the ones in the greek mythology as well as the ones that affect our PCs. But there are still many who use the term Virus to describe trojans. But they should know that Viruses are totally in their own class than trojans and worms. They are all malwares though.

So viruses, trojans and worms are different from each other. A virus is a malicious code or a software program that attaches itself with a file or a program and spreads leaving infections as it travels. It is mainly created with the intention to destroy or damage a machine and the datas unlike spywares which are created mainly with the intention of making money through capturing the browsing habits of the user and is thus mostly a unhealthy marketing practice.

A worm is a software program and a single computer can send thousands of worms since worms can replicate itself in a single computer and sent itself out using the file or information transport features of your computer.An email worm can send itself to all the people inyour address book.A copy of the worm scans the network for another machine that has a specific security hole. It copies itself to the new machine using the security hole, and then starts replicating from there, as well.

As many of you might know Trojan horses are software programs that comes disguised as something else. A program claiming to be an excellent tool for repairing your hard disk would be actually a program that contains a trojan. Trojan horses does not replicate itself. But on the computer that it resides it can open up backdoors so that a malicious person can take control of your PC etc:- through that back door. SOme less harmful trojans can change your desktop, hijack your browser etc:-


Types of Trojans.


Trojan horses are developing much faster than any other class of malicious codes.There are different types of trojans . Let us have a look at them:-

1.Backdoors: Alias: Hacker's remote access tool, Back door

Among the types of trojans this one is the most popular. A typical backdoor consists of two parts-client and server. The server is the one that is on the victim's machine and the client is the one the attacker uses to connect to the victim's machine. Some backdoors even have scanner utilities that allows the attacker to scan for machines installed with the server part. With the most advanced backdoors hackers can gain access to the machine and take full control including browsing through the victim's hard drive, receiving a screen shot and even use the webcam. But simple ones just allow upload and download and run files on the machine.

Most notorious backdoors: SubSeven, NetBus, Deep Throat, Back Orifice, Bionet, Master's Paradise.

2.Trojan downloader: Alias:Trojan Downloader, TROJAN-DWONLOADER, Win32.Trojan.Downloader, TrojanDownloader

This is a software program that connects to the internet on it's own and downloads program using the FTP or HTTP. This programs downloads the server part of backdoors that the attacker can use to connect to the victim's machine.

Notorious trojan downloaders are Aphex, Dlder, Small, WebDL.

3.Trojan-Spy and Trojan-PSW programs: This is classified into three categories:-

(a)Password stealing trojans: This can also be dropped by backdoors and some worms.It basically uses the keylogger to monitor the strokes and record it when the user has to to input login and passwords. This trojan can also send information about the victim's IP address etc:- to the hacker. The logged data is send over the net immediately or is submitted later. This type of trojans can install itself to the machine.

(b)Data stealing trojans: This looks for specific data or files on the victim's machine. They look for serial keys, or files where the user has stored his authentication informations etc:- And this is send over the Internet to the hacker. It can even send emails to the hacker in an excel file.

(c)Spy: This too can install on it's own and might be programmed in a such a way that it uninstalls itself after a certain period of time. The spy monitors the key strokes by using a key logger and also can spy on other activities on the victim's machine. And then this can sent this datas at certain intervals.

Well known Trojan-spy or Trojan PSW programs are Coced, Hooker, GOP, Kuang, Platan, Klogger.

4.Trojan Clickers: This kind of trojans hijacks the browser and re-directs it to specific urls. This can be used for the purpose of getting more traffic to a website and thus get more page impressions or hits and get revenue from ads or to mount a dos attack on a specific website or to lead the victim to a page where it has viruses, worms or trojans.

Trojan-Clicker.Win32.Agent.bm has been one of the trojans that has been making rounds in this category that disguises itself as the Microsoft Windows - Security Alert'. Once the user clicks on the "process with select of protection software button" it will redirect to a webpage that contains adwares. This trojan is also known as StartPage-EP , Troj/CWSC, TrojanClicker:Win32/Agent.BM , TR/StartPage.QC.2 , Trj/StartPage.HZ among the various AntiVirus makers.

5.Trojan Droppers: These are the ones used to install other trojans or other malwares onto the victim's machine. So, even if the victim does not install a malicious program on his own this one can install the other malwares on the machine.

6.Trojan Proxies: This one resides on the victim's machine and the hacker or a spammer can use this to re-direct their activities through the affected machine which would serve as a proxy. Thus a spammer or a hacker can have anonymous access to the Internet through the victim's PC.

7.Hearse: This is a new class of Trojans that is a combination of rootkits + trojans making it even more hard to detect the trojans. One of the trojans in this class is the Trojan-Spy.Win32.Bancos.pw which intercepts https traffic and was targetting two German banks. This kind of trojans can thus make the encrypted https traffic between the banks and the users insecure.

Trojans used in extortions


One of the most notorious trojans that has been used to blackmail the users is the Trojan.Win32.Krotten. The author of this one actually used 13 different versions to make it hard to detect. Instead of modifying the user files this one modified the system registry so that this was hard to delete. Since this modified the system registry it was possible to bring the system back to the state it was prior to getting infected. But the Trojan that followed this which was Gpcode created more havoc since it did not allow any way the the system could be brought back to it's prior state. Daideneg, Schoolboys, Cryzip, MayArchive are the other trojans that have been commonly used for blackmailing the victims.

Trojans and Mobile phones


Two trojans have been detected that effects the J2ME. One is the redbrowser that sends SMS to pay numbers without the users knowledge and consent. This trojan is capabale of running on a vast number of handsets that supports Java. The second trojan also sends SMS but to a particular number (1717) which is charged. Games.gsmland.ru was found to be the site that uses this number. Read about it here.

BotNets


Talking about Trojans one can't leave out the IRC Bots which have worm spreading capability - like the ZOTOB worm, MYTOB worm, and lots more which are worm trojans. Worm trojans combines the lethal affects of the self replicating nature of the worm with the malicious effects of Trojans. Thus they not only infect a lot of machines quickly but mulitplies in one single machine. The machine becomes a zombie computer. This allows the hacker or the attacker to sell the BOTNET (group of compromised computers) to the highest bidder. These are then used for Distributed denial of service (DDOS) attacks, spamming, massive browser hijacking etc:-

Trojans have been delivered via spam with attachments containing malicious code, or downloaded using a vulnerability exploit. It should be noted that malicious users are currently showing a preference for mass spamming over the use of exploits. Also some viruses and worms are known to drop server parts on the machine. Another way of getting to install programs with trojans is by installing programs that claims to be something else and thus coaxing the user into downloading and installing it on the machine.

Since trojans are in a different class from Viruses all AntiViruses does not detect all trojans. That is why it is advised to use Anti-trojan softwares along with AntiVirus softwares. Some of the best Antivirus softwares like Kaspersky, Bitdefender, Mcafee, Norton, Trend Micro, F-secure etc:- are good at detecting most of the trojans out there. But since trojans evolve a lot and the codes are modified more often it is always good to have an anti-trojan software along with your ANtiVirus tool.

Also since more and more trojans are appearing in the form of rootkits it is also good to have a Anti-Rootkit software too. Spywares are also a variation of trojans and so add to the tally an Anti-spyware since they too are in it's own class and thus you need a specialised tool for that. And ofcourse you need a firewall to monitor the ports and to see if any unwanted programs are accessing the net or whether your ports are being scanned too much. Appropriate links are provided under "related reading".

Let us have a look at some of the tools that specialise in negating Trojans:-


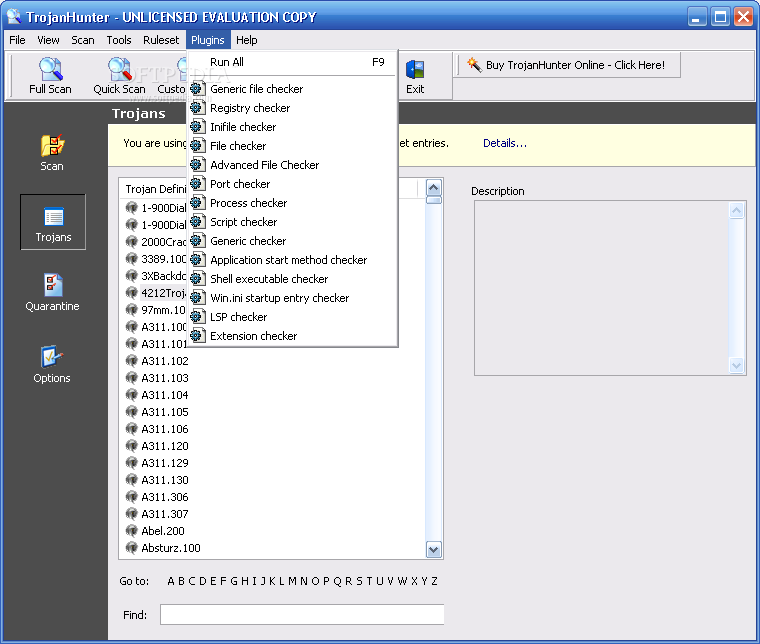
Trojan Hunter 4.6 - Paid ($49) (Free to try for 30 days) Download here.

This is a paid software and among the Anti-trojan softwares out there this one is the best. This is free to try for 30 days but unfortunately the trial version does not allow online updates. The scanning is very fast. The paid version has live update and a good heuristics(heuristics means instead of looking just for known signatures it analyses the behaviour of a file and get rids of the suspicious files. Thus any unknown trojans or malicious codes that shows malicious behaviour is taken care of. Among the softwares in the Anti-trojan category this is the best. And unlike some of the products available it is good at detecting polymorphic trojans. Polymorphic trojans are the ones that change their characterestics to avoid detection. The only bad side to this kind of detection is that sometimes it can give false alarms.


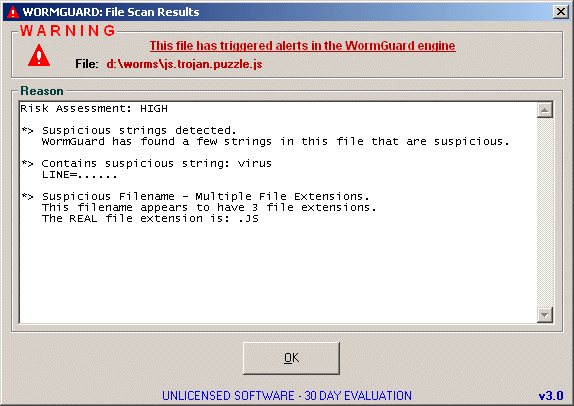
Wormguard 3 -PAID ($30) (Free to try for 30 days) Download here.

TDS 3 was one of the best Anti-trojans out there until the software maker discontinued it since they wanted to spend more time and resources on developing new products. Worm guard which is made by the same guys has been available since some time and the new improved version uses new deep-scanning generic detection technology and instead of depending on a data base to scan it thrives on having better heuristics and thus any trojans or worms that are new are identified and eliminated. This looks at the behaviour rather than the known signatures. Hence anything that has the characterestics linked to a trojan or a worm is spotted even if it is a new arrival which a software with poor heuristics that depends on a database might not spot until the database is updated.

But remember that a program that depends more on heuristics can trigger a lot of false alarms. A good program is the one that combines great database with great heuristics. And so you can expect some false alarms from this product. But use it to scan your PC and if you get an alarm scan the files with your updated anti-virus. This one does not use much resouces. And even whenever it gives an alarm it lets you have an idea of the file and which aspect of the file could be infected instead of just saying it is a virus. And even though this is not an out and out trojan hunter I have put this here since more and more trojans are taking up the Worm characterestics. Currently windows xp users and some other users are facing some compatibility issues (basically NIS issues) with this product. Version 4 will be available soon. So it might be better to wait until then.


AVG Anti-spyware (Formerly Ewido) –Free Download here.

Even though this is classified as Anti Spyware this works as a good Anti-trojan. The problem is that when it comes to the Anti-Trojan category not many free good free softwares are available. Ewido has always been concentrating on malwares especially in the class of trojans. And there is only a thin line between a spyware and a trojan. A spyware supposedly is installed on the PC with the "informed consent" of the user where as trojans trick users into installing the software. Carrying on with Ewido's tradition of being more of an Anti Malware software that concentrates on trojans and spywares the AVG anti-spyware does a good job for a free software. There is a paid version available of this product. The difference between the paid software and the free version is that there is no real time protection in the free version and no kernel level protection. However the on demand scanning is a good one. This product is also good at detecting polymorphic trojans.
Note: This works only with windows 2000 and above version. Among the free version this is the best.


a-squared - FREE Download here.

This is also a good Anti-trojan in the free category. This is actually the free version of Emsisoft's Anti-malware. The free version does not have real time protection, auto update and scheduled scan. But the data base is not compromised and you can manually update. However one should keep in mind that it is not a highly rated software. But again not much choices available in the free category when it comes to ANti-trojans. The scanning is not that fast either. use it in combination with another spyware and anti-trojan.

Like I mentioned earlier one should have a software that specialises in each category viz:- A firewall, an Anti-trojan (Ideally two), an AntiVIrus, an ANti Rootkit and a anti-spyware (Ideally two)

You can also find info on Anti-spywares and the HijackThis tool for advanced users here.

Related Reading:
Mobile phone malwares, blue tooth hacking and protection.
What are rootkits and related softwares
27steps to prevent virus
Free antivirus softwares
Zone Alarm firewall.

Thursday, November 23, 2006

Security Flaw in FireFox 2 allows Phishing Attacks.


There is a vulnerability in Firefox 2 that allows phishing attacks. The vulnerability is caused due to the Password Manager not properly checking the URL before automatically filling in saved user credentials into forms. This may be exploited to steal user credentials via malicious forms in the same domain. Secunia has reported this problem. Version 2.0 is affected and other versions might be affected too.

This problem seems to be the first major flaw reported in the version 2.o of firefox. There is a crash condition that was reported to exist in Firefox 2 recently but that was not a very common issue. But this is the first major flaw with the latest version. This problem has been dubbed as the reverse cross site request (RCSR) by the person who detected this flaw Mr. Robert Chapin.

Even though this problem is categorized as less critical by the Security firm Secunia the consequences of the flaw being exploited by the malicious people could be highly harmful to the users. Since a fake login page can be easily set up or a page that proxies traffic to a popular website like myspace can be set up and when the password is automatically filled in my the firefox password manager ( it does not verify the server to which te password is send ) it can be easily sniffed by the attacker. This can happen to users logging into blogs or other sites.

Surprisingly the same kind of problem exists with Internet Explorer 7 but since IE does a more thorough check before filling in forms it is vulnerable only if the reverse cross site request (RCSR) page (which is the attack page)appears on the same page as the login page.

Solution:
Disable the "Remember passwords for sites" option in the preferences.
Along with this disabling Password Manager is the other suggested solution.

This problem adds on to the recent multiple vulnerabilities spotted in older versions of FireFox and Sea monkey recently.
You can see that report here.

The other recent issues with Firefox has been reported here:-

Microsoft and Secunia at it again. And FireFox 2 too affected?
All IE 7 and Firefox 2 Vulnerabilities as of date.

Related Reading:-
Everything you wanna know about phishing attacks.

Wednesday, November 22, 2006

About Spywares and the best Anti-spywares.


As most of you might know spyware is a form of malware. Malwares are softwares that are used to intentionally collect information about a user or a machine or to damage a machine. The name malware was derived from combining the two words Malicious and Software. Virus, trojans, worms, spywares, adwares, rootkits are all malwares since they are all malicious sofwares. But spywares and adwares are written with the intention of making money where as viruses are mostly made with only a bad intention like destroying or damaging a computer.

Spywares are basically intended to track the user's browsing habits and report it to the source so that they can make targeted advertising campaigns. But it is highly harmful too. There are variations of spywares that can can even log what you type (key logging) and thus lead to all sorts of privacy problems and Identity thefts.


Spywares normally attach themselves to the browser and your browsing habits are send to the source so that they can collect information and using it for spamming and unhealthy marketing practices. The antiVirus tools do not detect spywares because they are not well defined as viruses , Trojans and worms. So that is why you need a tool that is specifically made to detect spywares.

Even though spywares are not destructive like a virus, trojans and worms it can slow down the pc and is harmful as it can contribute to identity theft. And these are send to the source over the net. So again that means it can also slow down the Internet connection as it uses the bandwidth. It can hijack a browser and stuff. More malicious variants attempt to intercept passwords or credit card numbers as a user enters them into a web form or other application.

Ways of getting a spyware, adware or both.

The main thing to be noticed is that most spywares collects information about a user or a machine with the "informed consent" of the user. This is done by writing those legal things on the software that you install it without being suspicious about it.

How many of you read the terms and conditions before clicking on the "I accept" button? This is why it is said that whenever you use a software that is not made by a reputable firm or well know firm you should read the terms and conditions before accepting it. The defense the spyware installing software manufacturers give is it was installed with the user consent and hence they escape any kind of legal pursuits against them.

But along with these kind of people who install spywares into your PC with your "informed consent" there are others who don't even mention that personal information will be collected.

So one of the most common way of getting a spyware is by using sharewares or bundled applications by companies whose reputation you don't even know about or companies that are well known (like Kazaa), who believes that collecting information about the user is alright. If you are installing those read the terms and conditions before doing it. But mind you, every person does not put it in the terms and conditions.

Programs like Kazaa, Download Accelarator etc:- are examples of softwares that combines spyware with adware.

Another way of getting a spyware is when you install programmes that gives you free cursors, free smileys, free screen savers etc:- Any free programs or internet speeding softwares (remember download accelarator?) etc:- which are not reputed should be dealt with caution. There are many good and highly reputed free programs out there but along with that you will also find these kind of malicious softwares trying to entice people into downloading with the main intention of collecting information rather than providing better service.

Going to sites that are unfamiliar with javascript and Active X turned on is another way of getting infected.

Using unfamiliar and unknown tools that autofills and using anonymous email sites that are non popular but looks enticing are all ways with which you can get these stuffs into your pc.

Now a days on every nook and corner of the net you would see ads saying "your computer is infected with spywares. Click here to remove it now" or "Download this program to remove it now". Well clicking on those kind of things can only lead to more spywares being installed on your pc.

Spywares are different from adwares. Adwares are softwares that automatically plays, displays or downloads advertisements to the machine with or without the user consent. There are spywares clubbed with adwares which is even more irritating.

While viruses are illegal without a doubt spywares are yet to be clubbed into that category with certainity. But whether all spywares fall into the illegal category or not, there is no doubt that they are harmful not only to the PC but to the privacy of the user too.

Spywares are everywhere now a days it is said that almost 90% of the computers in the world is infected by some sort of spyware.

Ok, now you have a fair idea as to how you can get a spyware or adware into your pc. Some of these same things are the means through which you can get other sorts of malwares (virus, trojans etc.) into your pc. But viruses and trojans are a different class and to prevent getting them you have to take steps far more than dealing with spywares or adwares. And since there codings are different an Antivirus cannot detect most of the spywares. Viruses are more well defined. But spywares are not. And that is why it is advised that it is always good to have more than two Anti spyware tools in your PC. Update your Anti spyware regularly and scan your PC atleast once a week.

Let us have a look at the well known Anti-spywares. These are free but they are highly efficient if not more
efficient than some of the paid Anti-Spyware tools out there.

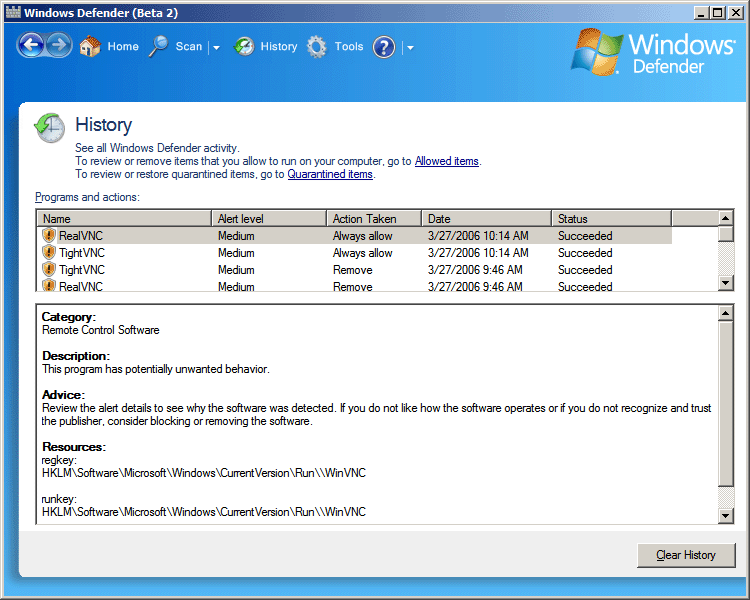
Windows Defender 1.1.1


This is the free Anti-spyware tool from Microsoft. So no wonder this requires Windows validation. This product was in the beta stage for a long time and now with this full version you get a great spyware detector that scans fast. It offers real-time protection. Whatever spywares the worldwide Spynet Community detects are constantly kept track of and the solutions are automatically downloaded to your PC through this program. It has advance protection and is a highly rated anti Spyware tool. Does not use much system resources.

Get it from CNET Download.com!


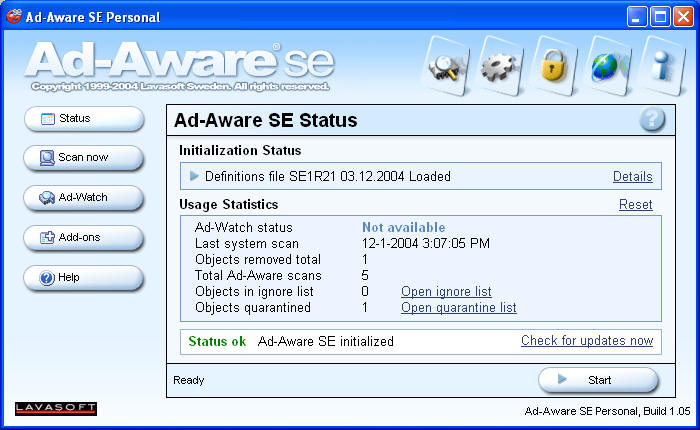
Ad-Aware


I remember using this prog a long time back since it was one of the first applications built to find and remove adware and spyware and it has come a long way since then. This was the prog. on which I saw the first spyware. It has a high number of definitions available and without doubt this is one of the best if not the best Anti spyware tool out there. No surprise that this got a 5/5 rating from the Cnet editors. It scans all modules loaded by processes, does the registry scan of multiple user accounts and the best part is that it uses less CPU and memory. It has a cool interface now and the scanning is fast. This guys have been in the business since a long time and hence they know how to bring out the best.

Get it from CNET Download.com!

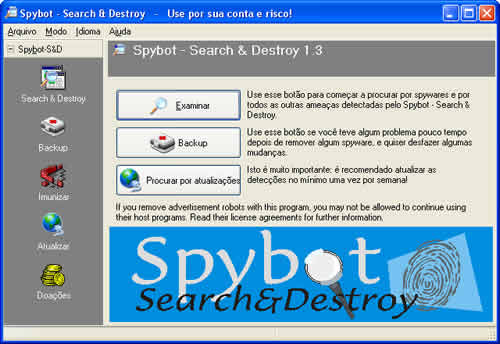
spybot search and destroy 1.4


One of the best free Anti spyware tools developed by Patrick Kolla. It has been highly rated by PC magazine and Cnet and was even metioned in BBC's fav tech related prog Click Online. Since this prog. came out a few years back I have started using this along with ad-aware. The scanning however is not as fast as windows defender and Ad Aware. To read more and download this great free tool go here.

AVG Anti-spyware (Formerly Ewido)

Ewido is already known around the world as a nice anti-malware (they always focus on not just spywares but on some trojans too, even though not as well covered as an ANtivirus would)tool. But they had some limitations. But after the merger with AVG it has got better. There is a paid version and free version available for this software. The free version does NOT allow automatic online-update, real-time monitoring of the entire system, self-protection at kernel layer guaranteeing gapless monitoring and does not allow you to use for commercial purposes. But neverthless with protection against 350,000 threats the free version without the mentioned feature is still a good utility to have. It does not take much system resources.

But AVG- Anti-spyware unlike the other three products listed here still has to earn a high reputation in the field of Anti-Spyware softwares.

Download the free version here.


All the above mentioned tools are great free Anti spyware tools but like I mentioned earlier when it comes to spyware it is always good to use more than one because spywares are not well defined.So a spyware that one prog might detect the other one might not. So use two Anti-Spywares in combination and chuck those fleas out of your PC. And remember that ideally one must have an Anti-virus, Anti-Trojan, Anti-spyware (Ideally two), Anti-rootkit and a firewall.

Special Mention: HijackThis


(Download HijackThis at the developer's website.)

This is a fantastic Anti-spyware/malware tool but it should be used only by advanced users. It the computer is still having problems after using Anti-spyware programs this tool can be used. This tool should be used only by someone who is experienced at reading the log outputs because fixing the wrong items can making your machine unbootable. What this tool basically does is to give you a list of what is found in registry or system files. It lets you review the logs and identify the problem. That way an experienced user can determine what is infecting the machine. More than a removal tool this serves as a tool that helps you diagonise the issue. It will remove the entries if you want to. But that won't cure the underlying problem.

Sometimes just removing the entries can solve some issues. But if you don't know what you are doing stay away from it. But still you can just run this program and look for any suspicious entries or if you really know what you are doing then you can use this to clean up the entries left behind after you have properly removed the hijacker or the malicious software using the right tool.

If you are not an expert One of the best thing to do is to run Hijack This on your machine and then post the log on one of the Hijack This forums available on the net where experienced people will give you advice. You can post your logs at Hijack This forums like the one you find here at this link.

Here is an excellent tutorial for using Hijack This.


Related reading:-
27 steps to prevent virus.
Rootkits and Anti Rootkits.
Best Free Antivirus programs.
Everything you wanna know about phishing attacks.(Identity theft)
keeping your password secure and Related softwares.

Monday, November 20, 2006

keeping your password secure and Related softwares.


Well there are many different things an Internet user has to follow when it comes to keeping their identity on the net safe from the identity theives etc:- There are some tips I had mentioned earlier in my article about how to protect yourself against phishing attacks. If you feel like reading that go here and look at the part where it says "Tips to protect yourself from phishing attacks". It covers almost every aspect about protecting yourself on the net from Identity thieves. However in this article I am going to focus only on the password aspect. Here are some tips that almost everyone knows (if not, everyone should know it) that are only related to getting a secure password and keeping it safe at your end. And also below you will see a list of related softwares.

1.Passwords should be atleast six character long.

2.Use a mix of alpabets, numbers and symbols (Aplhanumeric).

3.Don't use words that are contained in the dictionary. (since it will be easy for people to get it through a
dictionary attack)

4.Don't email or IM your password.

5.Don't store it on your computer.

6.Change it often. At least every 3 months.

7.Have different passwords for each site or mail address.

Ok, now almost everyone of you might know these things. But the problem is how would one ensure that these steps are adhered to. I mean like having different passwords for each site and that too complex passwords and yet not to store it somewhere? I mean that is quite challenging right? But here are some tools that will help you on that part. Not only will these tools help you generate complex passwords but it even fills out forms on the net for you in a secure way and you can store the passwords on your PC. Interested? Then read on.


PASSWORD GENERATORS.

1. Quicky Password Generator 1.2 (Free)

This one has got a 4.5 out of 5 from the users at download.com. Now when the users speak you know that it is not a gimmick. This prog can generate up to 5000 passwords of 4 to 20 characters in length at a time. There are options for alphanumeric, uppercase only, variable length, and special characters. It generates all unique passwords and will warn you if the character length is not long enough to give you unique passwords. It is very small in size (338.08K) too.

Get it from CNET Download.com!


2.Infinite Password Generator 2.2 (Free)

The download.com(Cnet) editors have given this a 4 out of 5 rating. YOu can generate different passwords for each site and you can access this utility by keying in your master password. So that means only you or someone else who knows the master password can acess this prog. Using only a master password which you need to remember and a keyword of your choice, you can use different passwords for every Web sites without remembering them all.

Get it from CNET Download.com!


UTILITIES THAT LETS YOU STORE PASSWORDS ON YOUR PC AND ALSO TO FILL IN FORMS.

1.RoboForm 6.7.9 ( Free to try)

This earned the coveted 5 out of 5 rating from the Cnet Editors. And also the users have given this a 4.5 rating out of 5. RoboForm memorizes each user name and password the first time you log into a site, then automatically supplies them when you return. This excellent prog. comes with a military level encryption. And all have to remember is your master password. All other passwords you generated using a password generator can be stored in this. It also fills out online forms.This prog. is a free to try software. Hence after 30 days some of the features will be disabled. If you have to buy it this costs $29.95

Get it from CNET Download.com!


2. Free Password Manager Plus 1.6.3(Free)

This is a very handy tool. Among the well rated free versions in the password storer category this is the one that stores passwords and also fills out forms. Roboform which I mentioned earlier is the other utility that offers this combination but it is just a free to try software..not free. So if you would like to have a free software that offers that sort of a combo then go for this one. The users have given this a 3.5/5 rating. This software protects your data by using 128-bit AES encryption and storing it on your own PC.

Get it from CNET Download.com!

Between Roboform and Free password manager it is better to go for Roboform even if it is free to try because you can still use Roboform after 30 days but with limited features. Like you can store a list of only 30 passwords. But for an average home user that would be more than necessary and enjoy the military level encryption it offers. Well, on the other hand you can try both and keep both if you like to.

Related reading:-
Everything you wanna know about phishing attacks(Identity theft).

Saturday, November 18, 2006

27 steps to prevent computer virus/Trojans.


picture courtesy-- London Times.
Read on to be aware of the 27 steps that will help you prevent your PC from getting infected with those deadly viruses. Some of these steps are common but many of them are not so common. So read carefully and stay protected.

1.Always be careful when it comes to e-mails that have attachments. If files contain EXE, COM or VBS as extensions then they are most likely able to cause harm to computers. Do not open it.

2.Do not open attachments when they are from people you do know, if the mail does not clearly refer to them. If they have a virus, then it can send mails to you. Therefore, only open attachments of which it makes sense to refer to.

3.Do not open video files from sources you are not sure. The new way of sending viruses is by using video files. It has already started so watch out for it. It was only recently that Anti-virus firm McAfee warned Windows users that the company had discovered a worm, dubbed W32/Realor, actively infecting Real Media files. The infected video files do not contain an exploit for the RealOne or Real players, but a hyperlink that points to a malicious website. It could be just the beginning to a new way of virus distribution.

4.While talking over the messenger use the file transfer option only if it is necessary and if you know the person at the other end well enough. Even if the person is known to you his computer might be infected with a virus. So make sure he too has an update anti-virus on his PC.

5.If a friend sends a file over the messenger do not open it unless it is the file you and your friend is sure is not infected.

6.Never dowload files send by unknown people.

7.Always have an up to date version of your messenger.

8.Be careful when trading any kind of files through your messenger or by any other means.

9.Always scan files on floppy disk or zip disk before using it. As you know an infected file from a disk that you have borrowed or which have been used on some another computer which has been infected can infect a clean PC.

10.Often attachments sent from a Mac will have not have any extensions. So in that case it is not possible to tell the type of the file. So as a precaution do not open attachments that has no extensions at all.

11.Always check the file extensions of any file arriving from a source.To see the file extensions Open Windows Explorer or My Computer. On the menu, choose View > Options to open the Options dialog box. If there is a View tab, click it. If there is not View tab, click the File Types tab. Then uncheck (by clicking its checkbox) "Hide file extensions for known file types." Click OK to close the dialog box. Usually by default windows does not show extensions. But once you checked the file extensions go back and hide the file extensions.

12.Even a picture file can be infected with a virus or Trojan. In 2004 a picture posted on the Usenet was infected with a trojan. It exploited the Internet Explorer. All the Antivirus programmes are capable of dealing with it now. But you never know what is in the making. Since it has been proved that it is possible it is good to be on the safer side. Any picture that floats in email or any unfamiliar sites which entices you to view it should be dealt with caution. Even though now a days a picture spreading a virus is only a remote possibility, the very reason that it is possible is a scary thing.

13.Word documents (.doc), Excel documents, and other files can contain macros that functions as viruses. But now a days all AntiVirus checks for these. But still excercise caution when it comes to unkown sources. A well known macro virus was the melissa virus and the cybernet virus.

14.Sometimes the virus warnings themselves are a farce. So think again before you start spreading the word or press the panic button at your end. Many reports of viruses are hoaxes. Many of these arrive through emails and instant messages. So if you have a doubt and before dealing with those kind of viruses double check it. The sites listed below are the ones you can use to verify a hoax message before you make sure they are for real. If you don't find them there google it.

F-secure's virus hoax related page.
Symantec's related page.
Mcafee's related page.

15.If you download a file from popular sites like Rapidshare before downloading look at the link and if you see the extensions like .exe, .scr, .bat etc:- be warned. SOmeone might load a file at Rapidshare or similar popular sites and spread the word luring you to download it. Or even after you download the zip or rar files look for the extension of the file it contains and scan it. If the extension sound fishy never touch it. For example a movie file with a .exe extension.

16.The file types that are the most dangerous are the files with the .exe, .com, .scr, .vbs, .cmd, .bat and .reg extensions because they contain programs and not documents. Take note of that and keep it in the back of your mind before opening it.

17.Do not visit websites that are unfamiliar. If you want to visit them turn off all your javascript options and Active X and cookies too. Many of the malicious websites asks the user to turn on the Java script or Active X. If a site is not a familiar one and has enticing words to invite you to the site and needs you to turn on the Java script and/or Active X then be careful. Some malicious sites can even infect you with a virus even if your java script and Active x is turned off. That is why you always need to have a up to date Anti-virus.

18.Don't visit warez sites especially key generators. A very small KB file that comes as a key generator once clicked can easily open up a can of worms or viruses.

19.There is always a danger of freely sharing computer programs and system disks, or downloading files and software through file-sharing applications such as BitTorrent, KaZaA etc:-

20.Excercise proper caution when using your personal disk space (e.g., floppy disks) on public computers or other computers that are used by more than one person.

21.Always running your Windows computer as an administrator or power user is not advised. A programme downloaded and executed when you have the administrator priveleges can even go to the root.

22.One of the ways to ensure that you don't get a rootkit virus is by accepting only digitally signed drivers.

23.Even AntiVirus softwares can have vulnerabilities. So always check for the latest news about the Antivirus software you are using. Very recently (nov.16 06) one of the top Antivirus progs, Panda, was found to be having highly critical vulnerabilities by the security firm Secunia. See the report here.

24.Remember Trojan.Bakloma.A. virus that came out in August 2006? If not let me refresh your memory. A link in the email claiming to be from Norton(Symantec) asked the users to download a removal tool for a new virus by following the link. Immediately as the user went to the site that was linked the virus Trojan.Bakloma.A. was automatically downloaded. So watch out for emails or suspicious links anywhere that asks you to update your Antivirus by following the link. All good Antivirus progs allows you to update through the software installed on your pc.

25.Use a firewall,Anti Spyware, Anti-Trojan, Anti-Virus and Anti Rootkits and update it everyday if possible.

26.Regulary update security patches from your browser and Operating system vendor.

27.Check for the latest virus threats by visiting the top ranked AntiVirus providers and security firms. Some of the sites you can visit are:-

Secunia the security firm.
Mcafee's threat center.
Bitdefender's info center.


Related Reading:-
What are Rootkit viruses and free RootKit detecting softwares.
Best Free Antivirus Softwares

Google